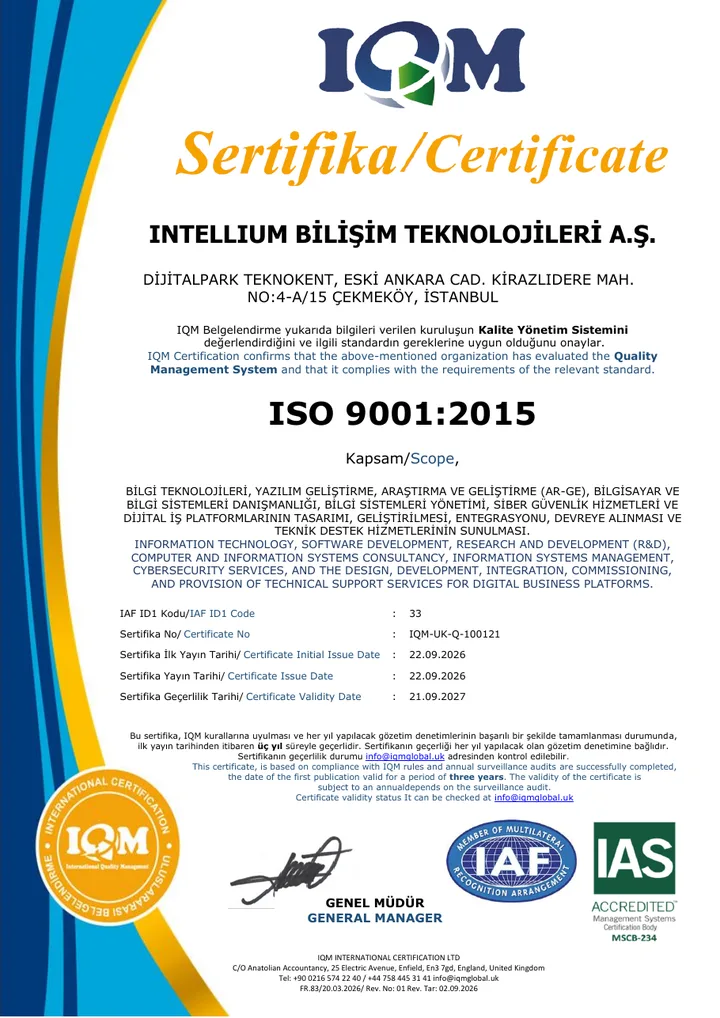
ISO 9001:2015
Quality Management System
- Certificate No
- IQM-UK-Q-100121
- Certification Body
- IQM International Certification Ltd
- Initial Issue Date
- 22 September 2026
- Valid Until
- 21 September 2027
Corporate
At Intellium, we continuously improve our quality and information security management systems to deliver our products and services at sustainable quality standards, protect our information assets and provide reliable service to our customers.
As Intellium Bilişim Teknolojileri A.Ş., we adopt the ISO 9001 Quality Management System approach to manage quality sustainably across the software, IT, consultancy and technology services we provide, to meet customer expectations and to continuously improve our processes.
Scope of Certification
Information Technology, Software Development, Research and Development (R&D), Computer and Information Systems Consultancy, Information Systems Management, Cybersecurity Services, and the Design, Development, Integration, Commissioning and Provision of Technical Support Services for Digital Business Platforms.
We run our quality management system on the principles of customer focus, process management and continual improvement.
We place customer needs and expectations at the centre of our processes and aim to continuously improve our products and services to ensure customer satisfaction.
We manage our software development, consultancy, project management, technical support and operational processes as defined, measurable and controlled processes.
We regularly evaluate the performance of our products, services and business processes, and carry out continual improvement based on results, feedback and improvement opportunities.
We systematically assess the risks that may affect our activities, plan the necessary measures and use emerging opportunities to improve our processes.
We monitor our quality objectives and process performance through defined indicators and use the results in management decisions and improvement activities.
Certificate No: IQM-UK-Q-100121
Valid Until: 21 September 2027
View certificateDiscover the information security management system and approach we apply to protect the confidentiality, integrity and availability of our information assets.
Scope of Certification
Management of Information Assets and Information Processing Processes Used Within the Scope of Information Technology, Software Development, Research and Development (R&D), Computer and Information Systems Consultancy, Information Systems Management, Cybersecurity Services, and the Design, Development, Integration, Operation and Technical Support Activities of Digital Business Platforms.
As Intellium Bilişim Teknolojileri A.Ş., we consider protecting the confidentiality, integrity and availability of information assets, managing information security risks systematically and continually improving our information security processes among our core principles.
We treat information security not only as a set of technical safeguards but as a holistic management approach that covers our people, processes, technologies, information assets and business partners.
We identify and classify our information assets and protect them with security controls proportionate to their risk levels, safeguarding information against unauthorised access, use, modification, loss or disclosure.
We apply appropriate technical and administrative controls to ensure that information is accessible only to authorised persons, remains accurate and complete, and is available when needed.
We identify and assess risks that may affect information security, and plan and implement the controls needed to keep them at acceptable levels.
We manage access to information systems and assets according to roles and authorisation levels, using access control and authorisation mechanisms to reduce the risk of unauthorised access.
We regularly evaluate the effectiveness of our information security processes and take action on identified nonconformities, incidents, risks and improvement opportunities.
Certificate No: IQM-UK-I-100121
Valid Until: 21 September 2027
View certificateOur management systems have been audited and certified by an independent certification body.
ISO 9001:2015
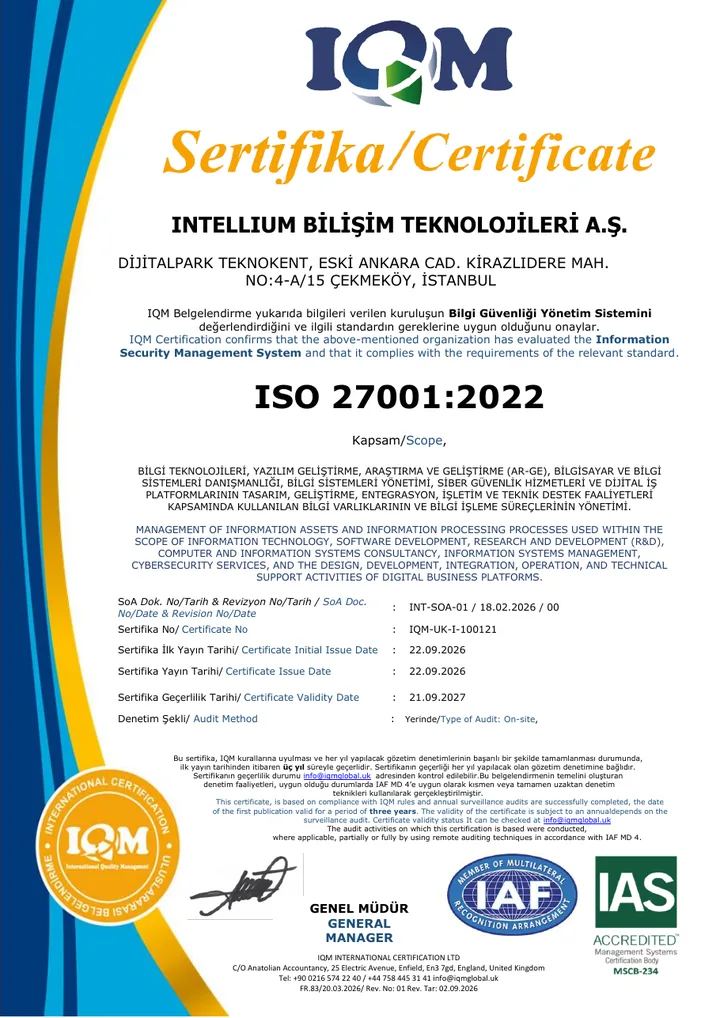
ISO/IEC 27001:2022
The validity of the certificates can be confirmed with the certification body (info@iqmglobal.uk).